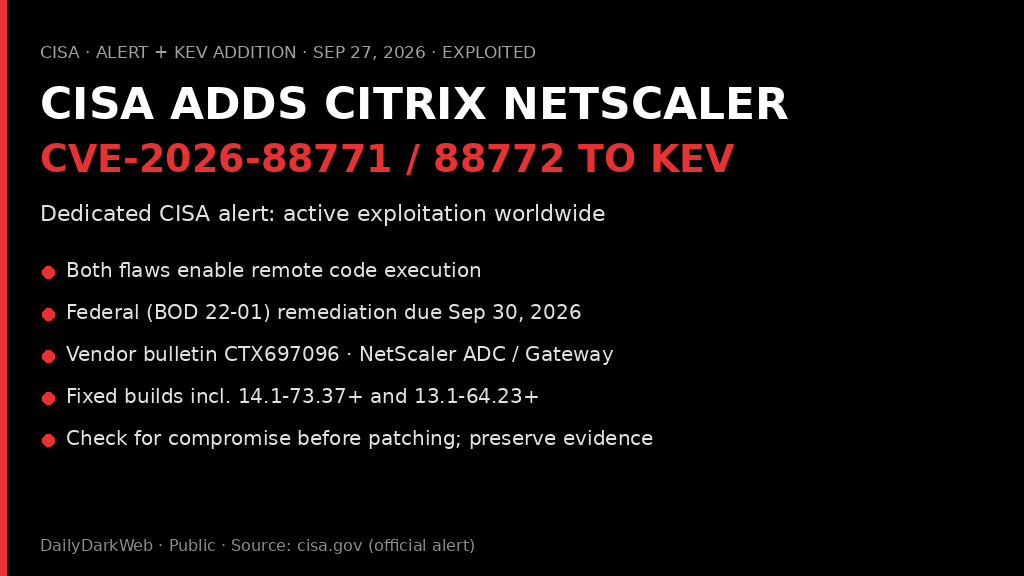
CISA adds two exploited Citrix NetScaler flaws to KEV catalog as active attacks hit unmitigated deployments
CISA added Citrix NetScaler flaws CVE-2026-88771 and CVE-2026-88772 to its KEV catalog after reports of active global exploitation, while Citrix urged affected customers to update unmitigated deployments as soon as possible.
TLDR
CISA has added Citrix NetScaler vulnerabilities CVE-2026-88771 and CVE-2026-88772 to its Known Exploited Vulnerabilities catalog based on evidence of active exploitation. In an alert, CISA said it received reports and partner threat intelligence confirming global exploitation by threat actors and advised users, where possible, to check for signs of compromise before patching and preserve forensic evidence if compromise is suspected. Citrix’s security bulletin said exploits have been observed on unmitigated NetScaler deployments and urged affected NetScaler ADC and NetScaler Gateway customers to install updated versions as soon as possible. Citrix identified CVE-2026-88771 as a remote code execution flaw affecting all deployments and CVE-2026-88772 as a memory overflow issue tied to DTLS configuration.
Combined views
7K
3 Sources, first seen 10h ago