Report
Two Citrix NetScaler flaws reportedly under active exploitation
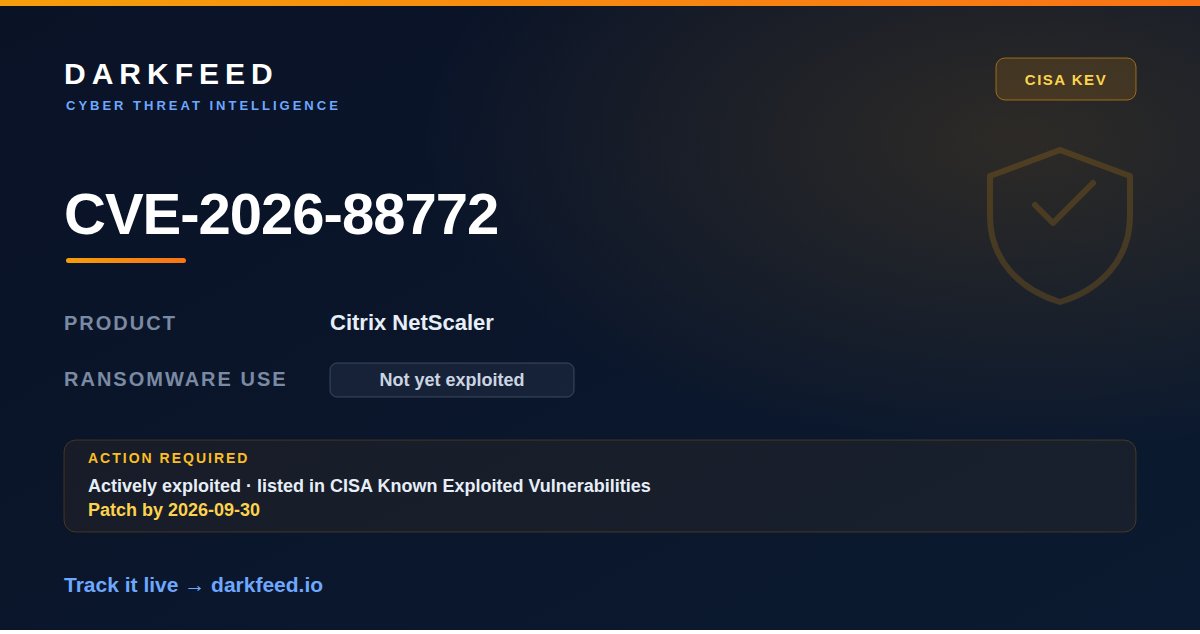
SecBriefs says CISA lists two NetScaler flaws amid active exploitation but identifies only CVE-2026-88771. A separate post names CVE-2026-88772 as actively exploited.
TLDR
SecBriefs says CISA lists two NetScaler flaws amid active exploitation but identifies only CVE-2026-88771. It urges organizations to inventory their appliances and check for both flaws rather than relying on one CVE. A separate post describes CVE-2026-88772 as an actively exploited memory-buffer flaw that risks remote code execution or denial of service, and urges vendor mitigations by September 30, 2026.
Combined views
1.3K
2 Sources, first seen 7h ago