Report
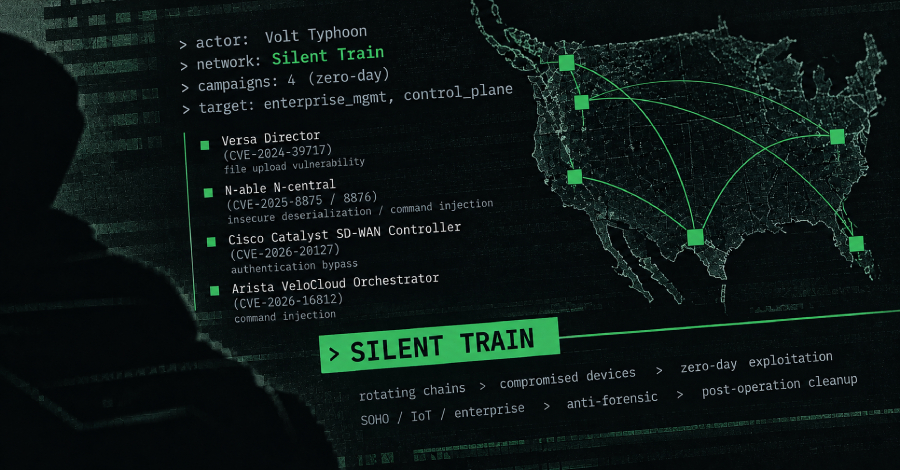
Volt Typhoon reportedly hid zero-day attacks behind Silent Train relay network
BleepingComputer reports Lumen’s Black Lotus Labs traced attacks on management systems through chains of compromised devices.


TLDR
Lumen’s Black Lotus Labs tracked Silent Train for three years and linked Volt Typhoon to at least four zero-day vulnerabilities targeting edge and management systems, BleepingComputer reports. The network routed attacks through compromised devices, with operators cleaning up disposable relays after sessions. Separately, SecurityWeek reports Cisco Talos found considerable infrastructure overlap with attackers targeting Cisco SD-WAN controllers, but did not identify them as Volt Typhoon.
Combined views
11.6K
2 Sources, first seen ago