Two NetScaler zero-days are under active exploitation as CISA adds both to KEV
BleepingComputer reported that Citrix confirmed CVE-2026-88771 and CVE-2026-88772 are being exploited against NetScaler devices, while CISA added both to its KEV catalog and said each can independently enable remote code execution.
TLDR
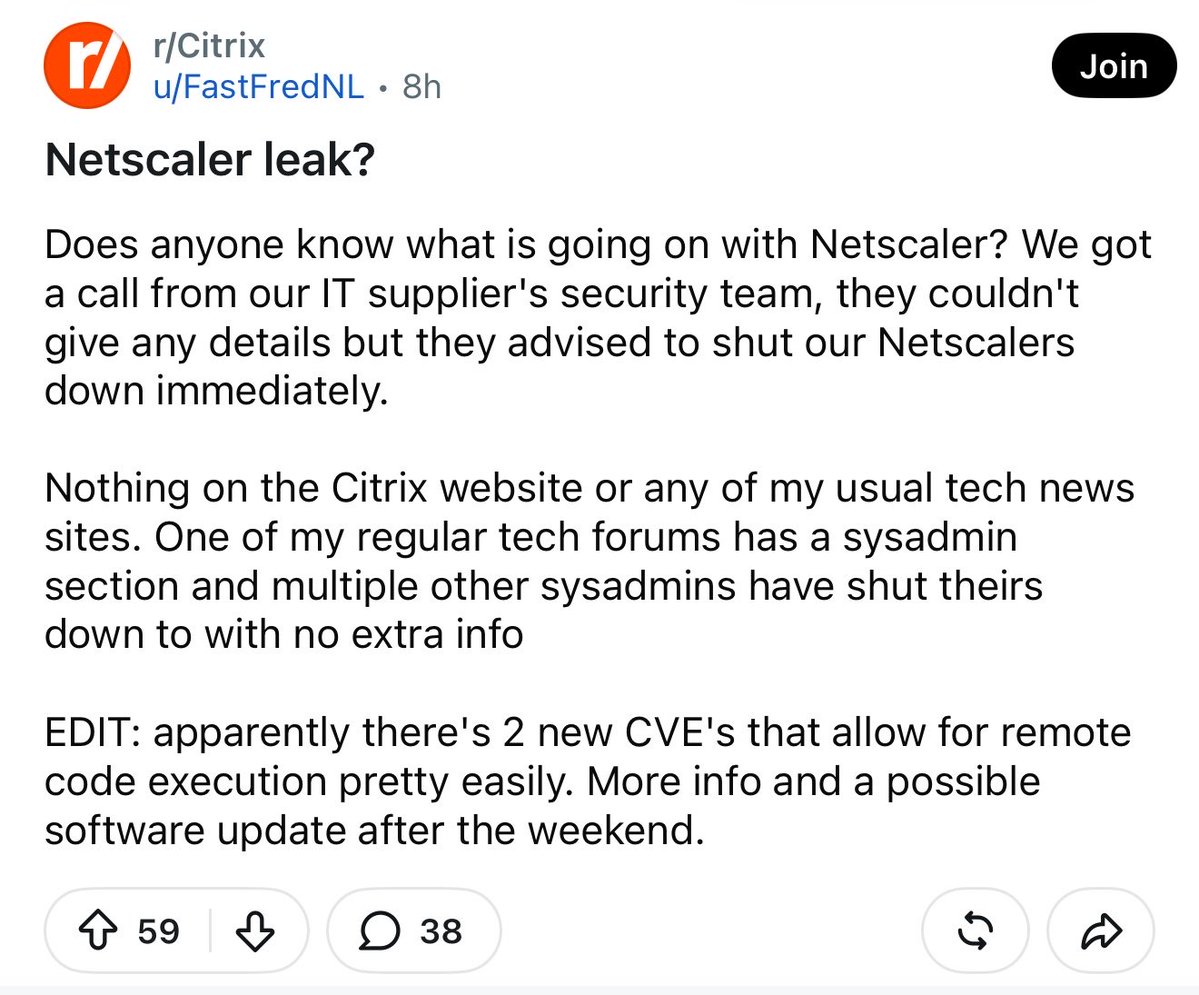
Citrix confirmed that CVE-2026-88771 and CVE-2026-88772 are being exploited in attacks against NetScaler devices, and CISA has added both to its Known Exploited Vulnerabilities Catalog, saying each can independently enable remote code execution. CISA advised organizations to check for signs of compromise before patching when possible and to preserve forensic evidence if compromise is suspected. Citrix has released security updates for affected NetScaler ADC and Gateway versions and urged customers to install them as soon as possible. The public warning followed earlier reported private notifications, including a reportedly sent Dutch NCSC pre-notification and reports that some organizations were being told to shut down NetScaler appliances.
Combined views
602.1K