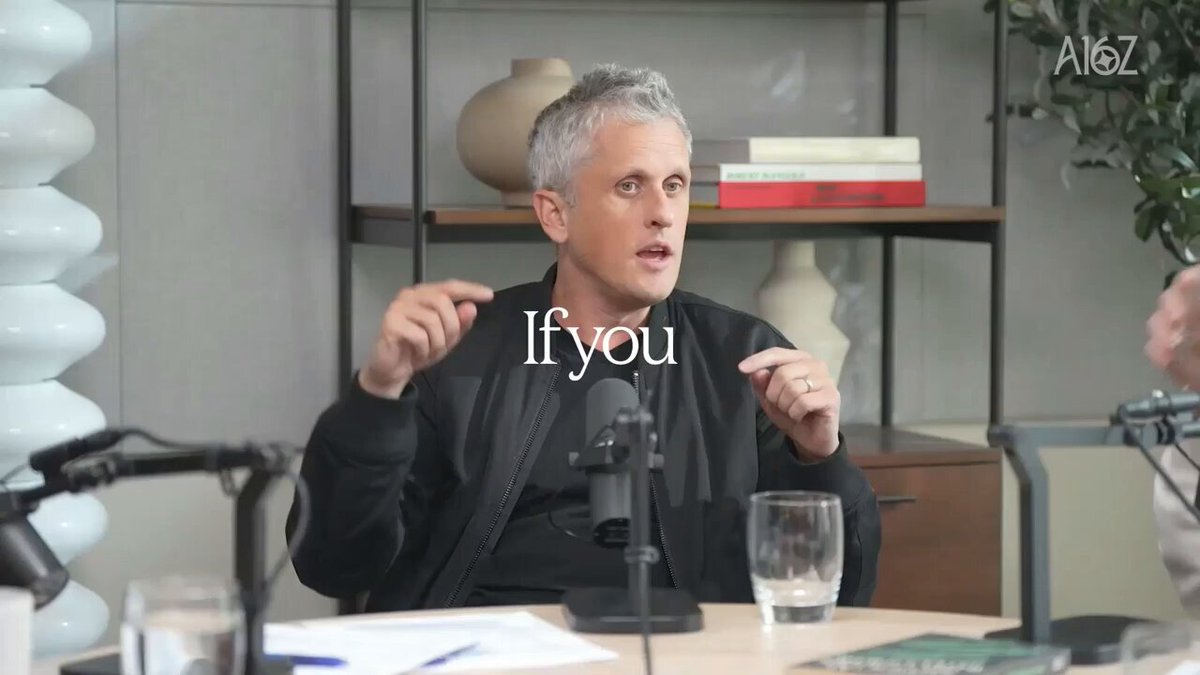
A new a16z panel discussion puts a practical question behind the AI-regulation fight: can policymakers write durable safety rules before the industry has a clear picture of how increasingly capable agents will fail in real deployments?
Host Erik Torenberg brought together Box CEO Aaron Levie, a16z general partner Martin Casado and former Microsoft Windows chief Steven Sinofsky. Their conversation ranges from frontier-model risk and the politics of the 2028 election to the less abstract security problems created when autonomous software receives access to company systems.
Agents change the threat model
The panelists argue that earlier technologies developed many of their safety standards after engineers and regulators observed concrete failure modes. They point to computer viruses, aviation and automobiles as examples, while warning that broad AI rules written too early could lock in the wrong assumptions.
Their agent-security argument is more immediate. Unlike an employee, an agent can run continuously, operate at enormous scale and probe systems repeatedly. In the panel's view, that could force companies to rethink permissions, authentication, operating-system boundaries and other parts of the security stack rather than treating an agent like an ordinary user with a faster interface.
The application layer may matter more
The discussion also separates frontier-model development from the software built around those models. The panelists expect a larger share of useful innovation to come from applications that turn models into decision engines and tools for specific jobs, rather than from labs pursuing ever more general systems alone.
That is a forecast, not a settled outcome. The episode does not announce a regulatory proposal or a new security standard; it lays out the design and policy questions companies will face as agents move from demonstrations into systems with real permissions and consequences.