• Home
  • Technology
  • Gaming
  • Entertainment
  • World & Business
  • Science
  • Sports
  • AI
HomeTechnologyGamingEntertainmentWorld & BusinessScienceSportsAI
Technology

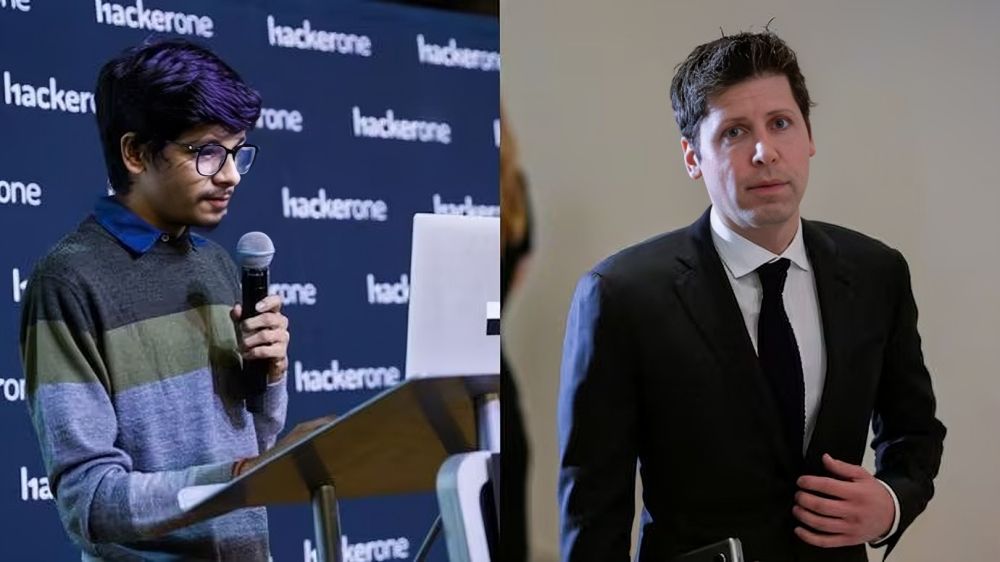
Hacktron AI researchers used Claude to exploit OpenAI vulnerabilities, earning $6,500 bug bounty

OpenAI paid $6,500 after the team disclosed chained vulnerabilities found with AI assistance.

Indian Tech & InfraIT
TNWTN
Avishka SrivastavaAS
10 Sources, 20d ago, first seen 20d ago

TLDR

Researchers from Hacktron used Anthropic's Claude to exploit a libheif image library issue and sign-in token misconfiguration. They accessed OpenAI employee accounts and internal GitHub repository within 72 hours at a cost of under $3,000 in tokens. The team disclosed the findings privately. OpenAI patched the issues in 14 hours and paid a $6,500 bug bounty. Reports state the weaknesses were not AI-related flaws.

Combined views

139.2K

10 Sources, first seen 20d ago

5.6K likes81 comments253 saves238 reposts
Combined views

139.2K

10 Sources, first seen 20d ago

5.6K likes81 comments253 saves238 reposts

Sentiment

Positive36.6%63.4%Negative

Summary

Many accounts criticized OpenAI’s $6,500 bug bounty as too low for the critical flaws found by Hacktron researchers, while others praised the responsible disclosure and Indian talent involved.

Based on 70 sentiment-bearing replies from 65 accounts across 5 conversations.

Featured Source

Sentiment

Positive36.6%63.4%Negative

Summary

Many accounts criticized OpenAI’s $6,500 bug bounty as too low for the critical flaws found by Hacktron researchers, while others praised the responsible disclosure and Indian talent involved.

Based on 70 sentiment-bearing replies from 65 accounts across 5 conversations.

Related

AI executives reportedly plan for backlash after a hypothetical catastrophic AI event

Axios reports planners consider a possible cyberattack that could cut off financial services, internet access, power or water.

OpenAI and Anthropic representatives pledge faster safety incident disclosures at Australian hearing

Techmeme, citing ABC, says OpenAI Chief Strategy Officer Jason Kwon made the pledge, with Anthropic representatives making similar pledges.

SoftBank completes $30 billion OpenAI investment; Broadcom agrees to lend Anthropic up to $42 billion

Reuters reports that Anthropic’s IPO filing identifies potential conflicts of interest in Broadcom’s roles as supplier and financing partner.

10 Sources

Indian Tech & Infra@IndianTechGuide🚨 Indian-origin researchers at AI startup Hacktron used Anthropic's Claude AI to hack into OpenAI’s codebase and ChatGPT accounts. They reported the security flaws to OpenAI. OpenAI then fixed the issues and paid Hacktron $6,500 (around ₹6.2 lakh) as a bug bounty.20d
TNW@thenextwebOpenAI paid them $6,500 for finding it. Three researchers disclosed privately, OpenAI patched in 14 hours, and neither weakness was an AI flaw. That is a bug bounty working, not a breach. https://thenextweb.com/news/hacktron-claude-openai-bug-bounty-6500-guardrails-paper20d
Avishka Srivastava@Avishka82$6500 is way too less for this, come on OpenAI you’re a multi-hundred-billion dollar company20d
Vikalp@SinghVikalpInteresting story of hugging face incident. Crazy the way AI agents are able to run own community.20d
AIBS News 24@AIBSNews24Indian-origin researchers at AI startup Hacktron used Anthropic's Claude AI to hack into OpenAI’s codebase and ChatGPT accounts. They reported the security flaws to OpenAI. OpenAI then fixed the issues and paid Hacktron $6,500 (around ₹6.2 lakh) as a bug bounty.20d
Ze Sir Kon Flakes@JonMontesDeOcaMay be .... There is some interwsr here and there to start to push for a "regulation" on AI ... with apocalyptic narrative . Someone needs something.20d
Ptaah the שדי@ShaddaiNoter@TheDefiantGhost It's called pentesting, you don't even know the name of hf before this story, and you think your opinion is significant20d
G-Axis@GAxisInfo🚨 Breaking: Researchers used Anthropic’s Claude AI to breach an OpenAI employee's account and access internal code, earning a $6,500 bug bounty reward. The Details: Security researchers from Hacktron spent less than $3,000 on AI tokens to automate a cross-platform exploit that ran for 72 hours. Is AI-powered hacking advancing faster than tech giants can patch vulnerabilities?20d
Bronson Schoen@BronsonSchoen@bradneuberg > Is this really a problem with leading edge AI, or a single vendor The HuggingFace incident broadly was completely unrelated to Irregular, and appears that the OpenAI models had been abusing various exploits for months, so I don’t think this at all explains the general problem20d
Defiant Ghost@TheDefiantGhostSam Altman CEO of OpenAI admitting the AI Agents incident. He himself calls it a “terrifying incident” , yet he seems remarkably nonchalant about it.20d
    • Home
    • Technology
    • Gaming
    • Entertainment
    • World & Business
    • Science
    • Sports
    • AI
    HacktronOpenAIClaude
    Anthropic

    10 Sources

    Indian Tech & Infra@IndianTechGuide🚨 Indian-origin researchers at AI startup Hacktron used Anthropic's Claude AI to hack into OpenAI’s codebase and ChatGPT accounts. They reported the security flaws to OpenAI. OpenAI then fixed the issues and paid Hacktron $6,500 (around ₹6.2 lakh) as a bug bounty.20d
    TNW@thenextwebOpenAI paid them $6,500 for finding it. Three researchers disclosed privately, OpenAI patched in 14 hours, and neither weakness was an AI flaw. That is a bug bounty working, not a breach. https://thenextweb.com/news/hacktron-claude-openai-bug-bounty-6500-guardrails-paper20d
    Avishka Srivastava@Avishka82$6500 is way too less for this, come on OpenAI you’re a multi-hundred-billion dollar company20d
    Vikalp@SinghVikalpInteresting story of hugging face incident. Crazy the way AI agents are able to run own community.20d
    AIBS News 24@AIBSNews24Indian-origin researchers at AI startup Hacktron used Anthropic's Claude AI to hack into OpenAI’s codebase and ChatGPT accounts. They reported the security flaws to OpenAI. OpenAI then fixed the issues and paid Hacktron $6,500 (around ₹6.2 lakh) as a bug bounty.20d
    Ze Sir Kon Flakes@JonMontesDeOcaMay be .... There is some interwsr here and there to start to push for a "regulation" on AI ... with apocalyptic narrative . Someone needs something.20d
    Ptaah the שדי@ShaddaiNoter@TheDefiantGhost It's called pentesting, you don't even know the name of hf before this story, and you think your opinion is significant20d
    G-Axis@GAxisInfo🚨 Breaking: Researchers used Anthropic’s Claude AI to breach an OpenAI employee's account and access internal code, earning a $6,500 bug bounty reward. The Details: Security researchers from Hacktron spent less than $3,000 on AI tokens to automate a cross-platform exploit that ran for 72 hours. Is AI-powered hacking advancing faster than tech giants can patch vulnerabilities?20d
    Bronson Schoen@BronsonSchoen@bradneuberg > Is this really a problem with leading edge AI, or a single vendor The HuggingFace incident broadly was completely unrelated to Irregular, and appears that the OpenAI models had been abusing various exploits for months, so I don’t think this at all explains the general problem20d
    Defiant Ghost@TheDefiantGhostSam Altman CEO of OpenAI admitting the AI Agents incident. He himself calls it a “terrifying incident” , yet he seems remarkably nonchalant about it.20d
    Today's Rank

    —

    Not ranked yet

    Today's Rank

    —

    Not ranked yet