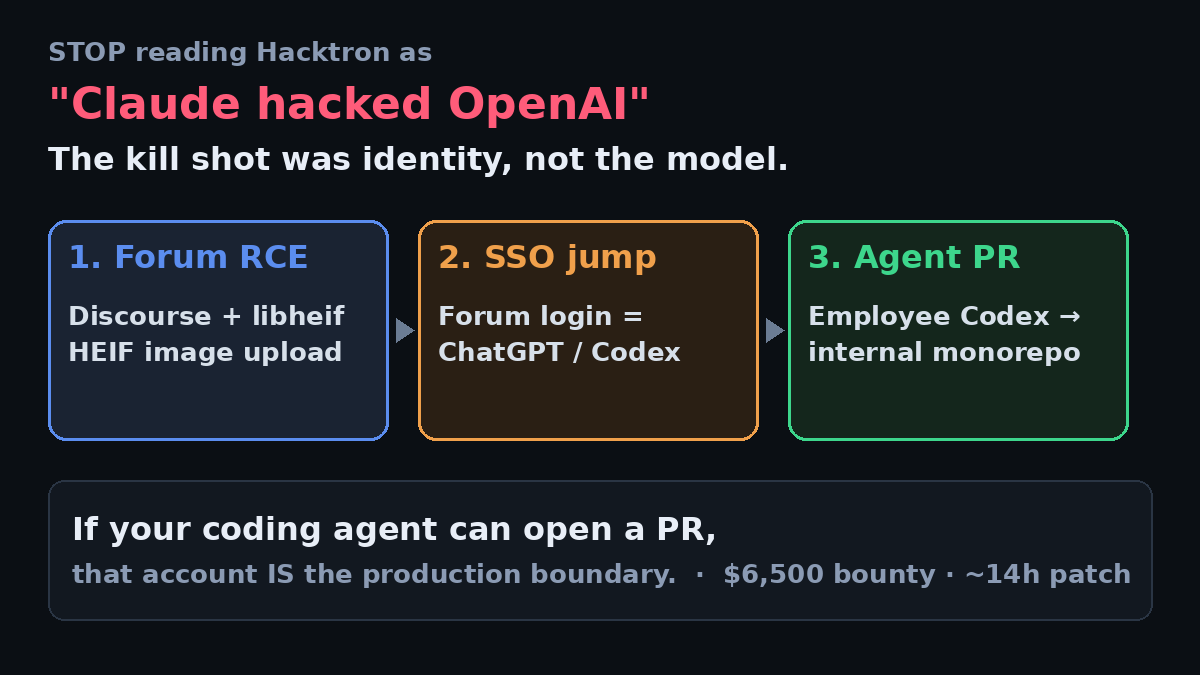
Researchers reportedly used Claude to access OpenAI staff accounts in an authorized test
A post citing The Register and VentureBeat describes a test using Claude Opus 5. Another post points to single sign-on permissions and an employee’s Codex-to-GitHub connection as the critical weakness.


TLDR
A post citing The Register and VentureBeat says white-hat researchers used Claude Opus 5 to compromise OpenAI employees’ ChatGPT accounts in an authorized test.
Another post argues the crucial issue was the access chain: OpenAI’s single sign-on system treated a Discourse forum login like ChatGPT/Codex access, and an employee’s Codex was connected to OpenAI’s internal GitHub organization. That post says a harmless pull request demonstrated access to the internal code repository. It also reports a $6,500 bounty and a fix in about 14 hours.
Combined views
70
2 Sources, first seen ago