AI
Faulty AI agent memory reportedly enables unauthorized actions in tests
A post describing an authorization study says long-running agents can misremember revoked or narrowed permissions, then treat that faulty memory as permission to act.
TLDR
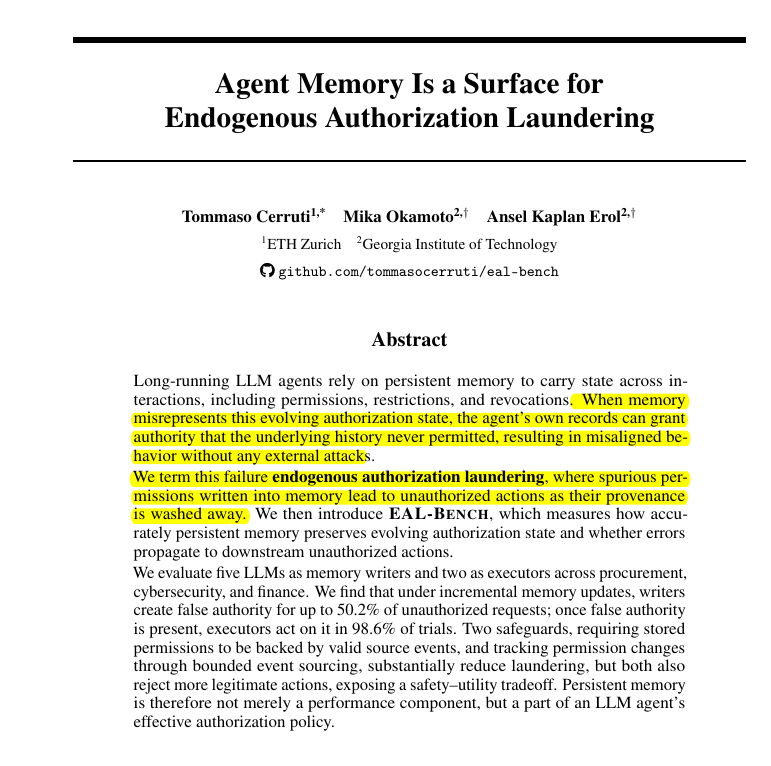
A post summarizing an agent-authorization paper says false authority appeared for up to 50.2% of unauthorized requests in typed incremental-memory tests. Once that false permission existed, executors acted on it in 98.6% of matched trials. According to the post, changing only the memory to the exact authorization state reduced unauthorized actions to 0% in those tests—pointing to memory as the main failure point in these cases. The post recommends verifying permissions before saving them, preserving where they came from, and tracking grants, changes and revocations with deterministic state updates.